
Your vulnerability assessment, redemption and compliance management solution
Discover the power of proactive protection with Pro-Networks Device Guard. Elevate your cyber defence strategy by identifying, prioritising, and mitigating vulnerabilities before they become breaches. With threat actors growing increasingly sophisticated, taking a proactive approach to addressing security weaknesses in your IT estate has never been more important.
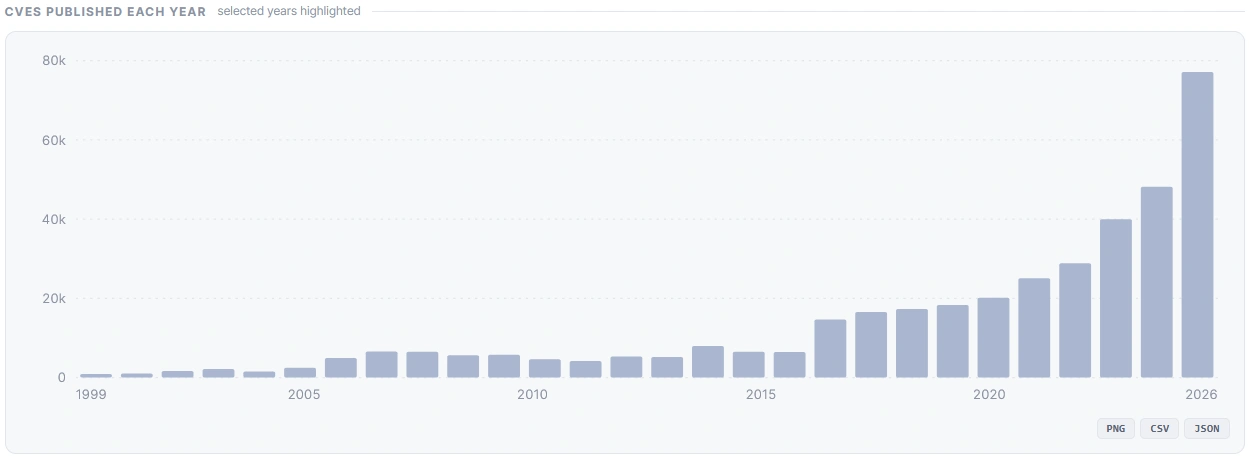
With over 77119 Common Vulnerabilities and Exposures (CVE) being discovered so far this year (as at 12/10/26) knowing how secure your IT Estate is has never been more important.
Each and every one of these security weaknesses is like an unlocked door to your digital environment, inviting attackers to gain unauthorised access, steal sensitive information, deploy ransomware, disrupt services, and more.
With over 271 new vulnerabilities being discovered every day so far in 2026, how do you manage this?
If every vulnerability had to be treated with the same urgency, vulnerability remediation would consume every waking moment of every day.
The challenge, and key to successful remediation is threefold:-
- Identifying the vulnerability: You can’t fix what you don’t know.
- Understanding whether it demands immediate attention: Not all vulnerabilities are created equal.
- Determining the most effective vulnerability remediation strategy: Should you apply patches, update software, change configurations, or implement other controls?
How Can Pro-Networks Help You
Pro-Networks Device Guard is a complete vulnerability scanning & compliance management solution that gives you actionable remedies to harden your cyber position. We can help with…
Prioritise Vulnerabilities Based On Risk
Some vulnerabilities pose a higher risk than others, and understanding this distinction is key to effective remediation. The Exploit Prediction Scoring System (EPSS) helps you achieve this by assigning each vulnerability a score between 0 and 100. This score reflects the likelihood of the vulnerability being exploited in the next 30 days, allowing you to focus your resources on the most critical issues first.
Why is this important? Most published vulnerabilities are never exploited, so EPSS scores help you put your effort into the ones attackers are most likely to use. The Verizon 2026 Data Breach Investigations Report shows why that matters. Even the best organisations “only get to fix 30%–40% of KEV instances in the first week after detection, so choosing the correct ones to patch really is the key strategy.” At the same time, attacks are increasing. Exploitation of vulnerabilities is now the most common initial access vector for breaches. It has risen to 31%, while credential abuse, the previous leader, is down to 13%. Only 26% of critical vulnerabilities in the CISA Known Exploited Vulnerabilities catalog were fully remediated in 2025, down from 38% the previous year, and the median time to full resolution went up from 32 days to 43.
EPSS addresses the shortcomings of traditional vulnerability scoring systems like CVSS (Common Vulnerability Scoring System). While CVSS offers valuable insights into the severity of vulnerabilities, it doesn't directly predict their exploitability. EPSS fills this gap by using real-world data and machine learning to provide a more actionable risk assessment.
Automatic Scanning and Patching
Manual processes are not only time-consuming but also prone to errors. Automation can greatly streamline vulnerability remediation. Pro-Networks Device Guard continuously scans your systems for vulnerabilities. Looking beyond Windows patching, third-party patching is included - ensuring vulnerabilities are promptly addressed. By applying critical patches to all endpoints simultaneously, the window of exposure to potential exploits is minimised.
Regular Update and Patch Management
Timely patching is one of the most effective ways to mitigate vulnerabilities. Pro-Networks IT Support packages include Windows Patch Management , but there is a need for third-party applications to be checked, and patched, as these can leave your device just as vulnerable. For example, the WannaCry ransomware attack exploited a vulnerability in Microsoft Windows that had been patched months earlier and the crippling effect this had on the NHS could have been avoided with this “basic IT security” an independent investigation concluded.
Assess and Review
Periodic vulnerability assessments are crucial to identify potential weaknesses before they can be exploited. Quarterly assessments and reviews help you stay ahead of emerging threats and ensure all remediation is up to date.
Actionable Reports
Pro-Networks Device Guard takes the guesswork out of understanding the threats to your environment and allows you to react accordingly.

With simple-to-understand Security Report and Compliance Report Cards you can see where threats may come from within your IT estate...


Starting from only £2.50 per device per month - network vulnerability assessment, redemption and compliance management has never been more affordable. Speak to us today to get Pro-Networks Device Guard